Virtual Context Engine
The Virtual Context Engine enables the creation of multiple logically separated firewall contexts within supported infrastructure. This capability can support multi-segment or multi-tenant security requirements.
It allows administrators to create and manage multiple virtual firewall instances (contexts) within a single root Next-Generation Firewall (NGFW).
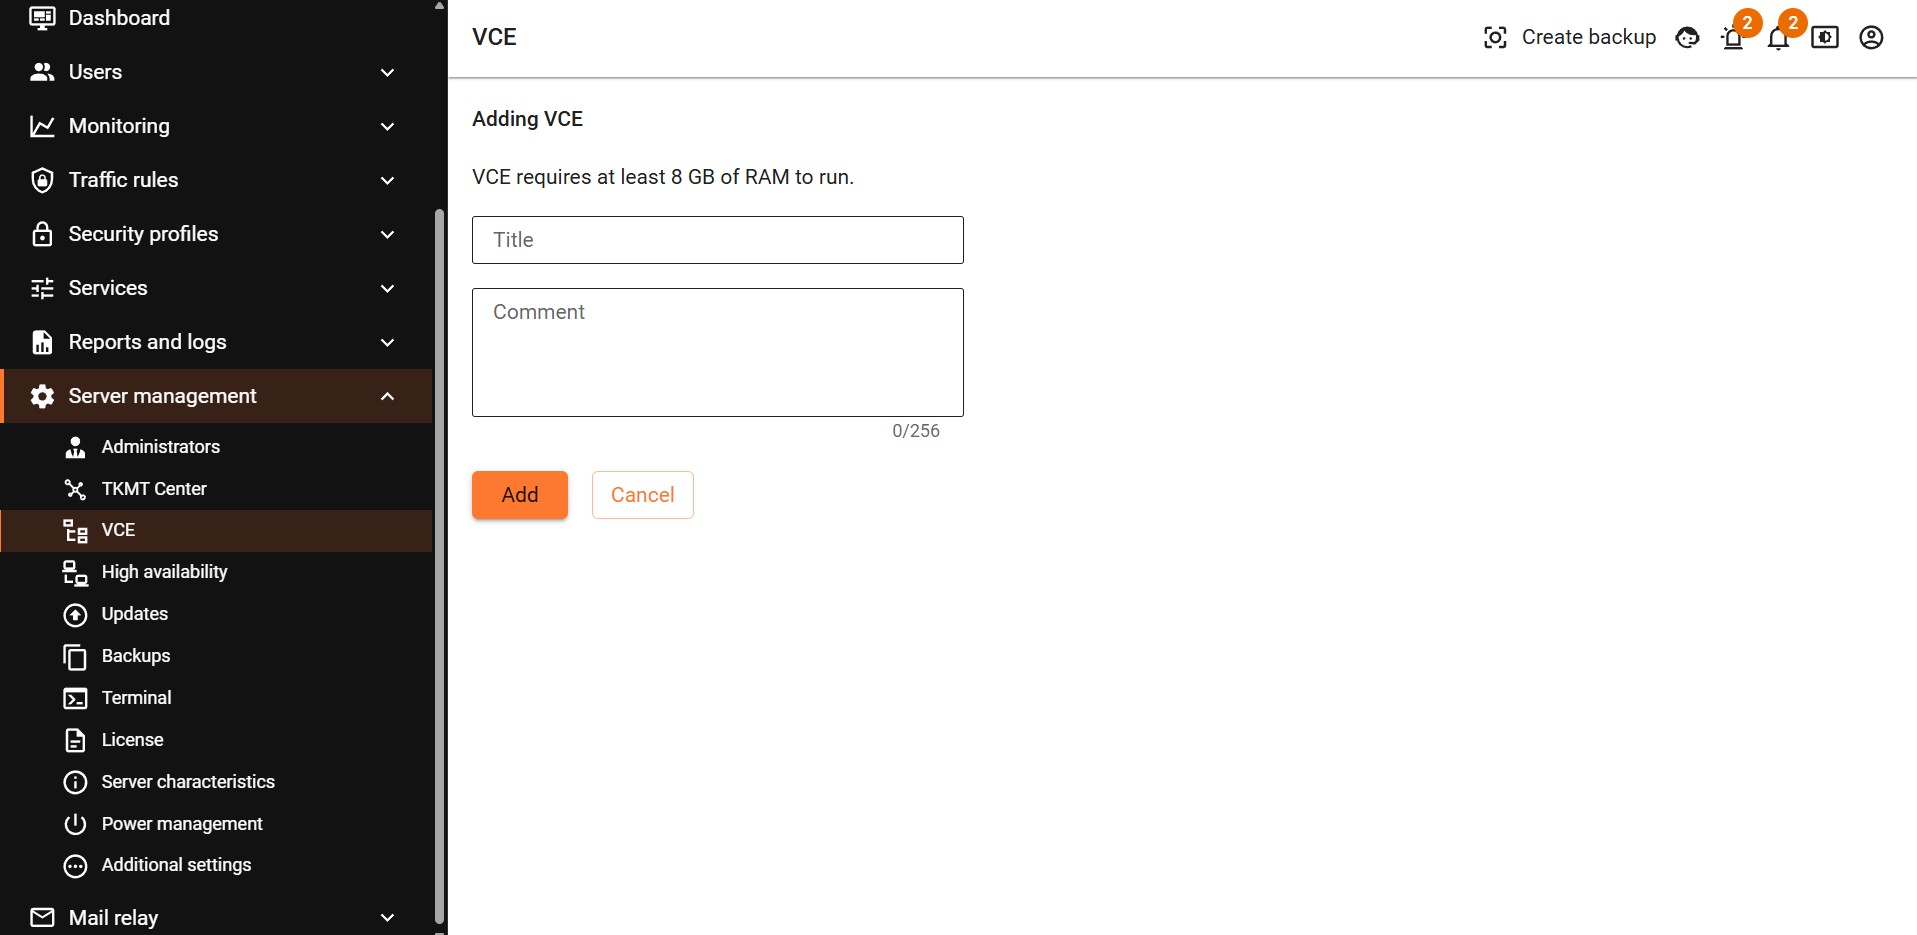
- Split a single local network into several independent networks with complete traffic isolation between them. Communication between the root server and the virtual contexts is accomplished via external network bridges.
- Create security policies and objects individually for each network.
- Control access and manage VCE independently.